How To Avoid Email Scams and Verify Authenticity
Electronic mail remains one of the primary backbones of digital communication, connecting people across continents for commerce, business operations, and personal correspondence. Yet because email was originally engineered decades ago as an open and accessible protocol rooted in implicit trust between the sender and the recipient, it possesses structural vulnerabilities that bad actors exploit every day. Because transmitting messages at massive scale costs virtually nothing, cybercriminals target everyone from casual users who rarely check their accounts to chief executives running multinational corporations.
The danger is not merely an occasional nuisance confined to junk folders. Fraudulent correspondence increasingly mimics everyday service providers, trusted online retailers, payment processors, and utilities with alarming precision. Recognizing how these deceptive campaigns operate, dispelling common myths about digital infection, and establishing rigorous habits for auditing messages are vital requirements for anyone navigating the modern internet.
Key takeaways
- More than 80 percent of companies and millions of individual consumers face phishing attacks annually.
- Simply reading the text of an email will not infect a machine, but launching untrusted attachments can immediately trigger malware.
- Display names often hide fraudulent sender addresses that feature scrambled alphanumeric characters rather than legitimate corporate domains.
- Hovering over embedded links before clicking exposes deceptive destination URLs that steer users toward credential-harvesting websites.
- Segmenting inboxes by keeping a dedicated address exclusively for banking minimizes exposure from routine data leaks.
The Modern Threat Landscape: Why Email Scams Proliferate
The scale of fraudulent digital messaging is staggering. Security industry metrics indicate that more than 80 percent of companies and millions of private citizens encounter phishing attempts each year. Approximately one percent of all electronic correspondence traversing global networks originates from malicious actors seeking to harvest private contact records, banking numbers, and social security numbers. For an average inbox owner, this volume translates to being targeted by roughly one scam attempt every single day.
Estimates show that only three percent of people can consistently identify a phishing attempt each time it appears.
Despite the prevalence of these lures, human detection rates remain perilously low. Research reveals that only three percent of people successfully identify a phishing attempt every time one appears. Compounding this challenge, approximately one-third of all fraudulent emails sent are opened by their recipients, with a substantial portion resulting in hostile malware installations. Because inbox filters cannot intercept every cleverly crafted dispatch, attackers treat email as their highest-yield vector for unauthorized entry.
Deception Mechanics: How Phishing Attacks Infiltrate Inboxes
Scam operators depend on social engineering to bypass analytical thinking. By fabricating urgent notices—such as an alleged account suspension, an unrecognized billing charge, or an expired security setting—attackers push recipients into making reactive decisions. The primary goal is almost always unauthorized extraction: capturing login credentials, collecting payment card numbers, or establishing covert access to the victim's local operating system.
A widespread misconception among users is that the mere act of viewing an email's body text can infect a device with viruses. Reading standard text will not trigger malicious code. Instead, technical risk manifests when users interact with untrusted payloads: either by launching embedded attachments or by clicking outward hyperlinks designed to mimic authorized web portals. Understanding the distinct mechanisms behind these delivery channels allows users to interact with their mailboxes without undue panic while maintaining robust digital hygiene.
| Attack Vector | Primary Threat Mechanism | Immediate Verification Check |
|---|---|---|
| Display Name Spoofing | Masks an illegitimate sender identity with a trusted corporate title. | Expand header details to examine the domain suffix after the @ symbol. |
| Deceptive Hyperlinks | Routes traffic to mirror web pages designed to harvest credentials. | Hover cursor over the text or button to preview the true destination URL. |
| Hostile File Attachments | Executes macros, scripts, or installer payloads upon launch. | Inspect file extensions and verify sender identity via alternate channels. |
| Social Engineering Panics | Pressures victims into revealing sensitive personal data like banking numbers. | Review tone, urgency, and editorial grammar before responding. |
Essential Strategies for Verifying Message Authenticity
Developing dependable evaluation habits protects personal identities and organizational networks from intrusion. When an unexpected message appears in an inbox, applying specific verification standards prevents deceptive dispatches from achieving their objectives.
Verifying the Sender's Actual Domain Address
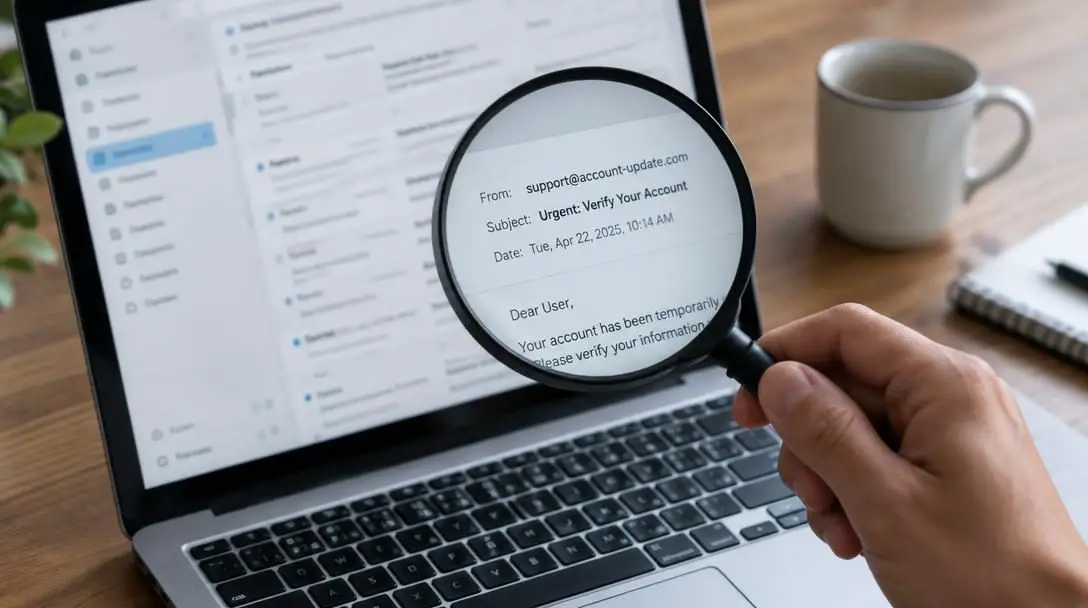
Inboxes prioritize user-friendly display headers, often showing labels like Amazon Customer Service or Paypal Support in prominent text. Scammers manipulate these fields to disguise hostile origins. Always expand the full technical header to review the sending domain. Legitimate corporate dispatches will conclude with the organization's verified domain name, such as @amazon.com or @paypal.com. Counterfeit dispatches routinely originate from arbitrary, free webmail platforms or utilize a random scramble of numbers and letters designed to confuse casual observers.
Inspecting Embedded Hyperlinks Before Clicking
Hyperlinks are frequently engineered to look harmless while directing web traffic to malicious destinations. Never click a link in an unverified email. Instead, hover your mouse cursor over the anchor text or interactive button without pressing it. A small preview tooltip will appear at the bottom of the window displaying the actual destination address. If a message claiming to originate from PayPal displays a destination URL that does not lead directly to paypal.com, the communication is guaranteed to be a fraudulent trap.
Scrutinizing Content for Editorial and Grammatical Errors
Major corporate enterprises invest heavily in professional copywriters and multi-tiered editorial workflows to ensure outgoing correspondence meets rigorous linguistic standards. Consequently, legitimate mass correspondence rarely contains typographical errors, broken syntax, or spelling mistakes. Conversely, many deceptive campaigns originate overseas where operators may lack fluent command of the language they are targeting. Glaring editorial mistakes, awkward sentence structures, and improper punctuation remain reliable signatures of unauthorized correspondence.
Isolating Critical Accounts Through Strategic Email Segmentation
Using a solitary email address for every online activity creates severe operational risk. If an address used for public forums, promotional newsletters, and retail purchases is leaked in a third-party corporate breach, malicious actors can leverage that identifier to target personal banking profiles. Users can build defense-in-depth by maintaining separate email accounts: reserving one dedicated address strictly for sensitive banking numbers and essential financial profiles, while utilizing secondary accounts for day-to-day internet registrations and public messaging.
Fortifying Defenses with Antivirus and Firewall Protections
Security software providers continually publish definitions and monitoring tools engineered to detect contemporary cyber exploits. Maintaining an active personal firewall combined with up-to-date antimalware and antivirus software establishes a critical secondary safety net. If a deceptive message tricks a user into interacting with a hazardous file, modern defensive software can identify malicious signatures, screen outbound network traffic, and quarantine the hostile process before system integrity is compromised.
Quarantining Unexpected File Attachments
Hostile payloads rarely appear as overt system installers; they are frequently disguised as routine invoices, tracking receipts, or office documents. Because simply reading an email's text poses no malware hazard while opening attachments does, users must treat every unexpected attachment as dangerous. Never launch or extract files received from unknown senders without first verifying the transmission through an independent, verified communication channel.
Common Inbox Mistakes to Eliminate
Falling for an inbox exploit does not require technical ignorance; it often happens during busy workdays when users are scanning messages quickly. Being mindful of these routine oversights significantly lowers your risk profile:
- Relying exclusively on the friendly display name: Accepting the surface identity shown in an inbox preview without checking the technical address beneath allows attackers to disguise themselves as reputable service providers.
- Opening embedded links in haste: Clicking buttons to resolve purported delivery failures, account suspensions, or password resets without previewing the destination address enables deceptive redirects.
- Launching attachments out of curiosity: Interacting with unprompted documents, billing notices, or compressed files assumes the sender is benevolent, exposing the local system to executable code.
- Ignoring grammatical and structural warning signs: Overlooking irregular syntax, awkward vocabulary, or unusual formatting permits obvious foreign scams to evade human scrutiny.
- Consolidating all services into a single inbox: Sharing one primary email address across retail outlets, promotional newsletters, and core banking portals maximizes exposure when consumer databases leak.
- Letting defensive software lapse: Disabling automatic security patches or running outdated antimalware engines leaves endpoints vulnerable to newly compiled evasion tactics.
How to Audit a Suspicious Message Step by Step
When an unexpected or alarming notification lands in your inbox, following a systematic verification procedure prevents emotional manipulation and stops unauthorized account compromise.
- Halt immediate interaction: Do not click embedded buttons, open downloadable attachments, or reply directly to the sender.
- Examine the expanded sender domain: Inspect the full address behind the display name to verify that the domain suffix precisely matches the official entity rather than an unorganized scramble of letters.
- Preview destination links: Position the cursor over all embedded URLs to verify whether the destination points to the company's verified web address.
- Analyze the language and urgency: Look for aggressive ultimatums, threats of immediate suspension, and obvious grammatical mistakes that indicate an offshore social engineering scheme.
- Verify independently outside the email: If the message claims your banking numbers or account status require attention, launch a web browser separately, enter the verified URL manually, and check your dashboard directly.
Frequently asked questions
Can opening a scam email infect my computer with malware?
No. Reading the standard text inside an email will not infect your system with viruses or malware. The threat arises when users download or open untrusted attachments containing executable payloads, or when they click deceptive links that route them to credential-stealing websites.
Does opening an email notify the scammer that my account is active?
Yes, it can. Many spam operations embed invisible tracking pixels or utilize read receipts that ping the sender's server when the email loads. This informs the attacker that the address belongs to a real, attentive person, which often results in an increase in subsequent scam attempts.
How can I tell if an email from PayPal or Amazon is authentic?
Check the actual sender address rather than just the display name. Legitimate corporate notices will originate from domains that end strictly in @paypal.com or @amazon.com rather than a scrambled sequence of alphanumeric characters. Additionally, hovering over links inside the message will confirm whether the URL genuinely points to the company's authentic website.
Why do so many scam emails have poor grammar and spelling?
Legitimate organizations employ professional writers and editors to ensure customer-facing communications are free of errors. Many scam operations originate from foreign countries where the operators are not native speakers of the target audience's language, resulting in awkward phrasing and conspicuous typographical mistakes.
What is email segmentation and why is it recommended?
Email segmentation involves using distinct email addresses for different online activities. By keeping one address strictly for sensitive profiles like personal banking and utilizing alternative addresses for casual web sign-ups, social media, and newsletters, you insulate your critical financial identities if a public database suffers a breach.
The Bottom Line
Email security is fundamentally an ongoing discipline rather than a temporary fix. Because scam campaigns evolve constantly to circumvent automated email filters, individual discernment serves as the strongest defensive barrier against inbox fraud. Adopting a zero-trust mindset toward unexpected notifications eliminates the majority of hazards before they develop into active security incidents.
Whenever an incoming dispatch requests your contact information, banking numbers, or social security number, never interact through the pathways provided within the message itself. By inspecting sending domains, hovering over hyperlinks, scrutinizing editorial quality, keeping defensive software updated, and accessing platforms exclusively through independent browser tabs, you maintain complete authority over your digital footprint and personal data.